Enterprise AI Security: Protect Your Data and Processes
Connecting AI to your documents, WhatsApp, or CRM requires controlling what information it accesses and what actions it takes. Learn how to evaluate vendors, protect data, and launch a pilot with clear boundaries.
Enterprise AI security starts before you connect a model to your CRM, ERP, or internal documents. The question is not just whether the tool is secure, but what information it will receive, who can access it, and what actions it will be allowed to take. A useful assistant can become a source of exposure if it inherits excessive permissions.
For a Mexican business, protecting information means safeguarding personal data, trade secrets, and business continuity. This guide brings together criteria for evaluating an enterprise AI integration without limiting its benefits: less manual work and better access to knowledge, with clearly defined responsibilities and boundaries.
1. Enterprise AI security: identify data and risks
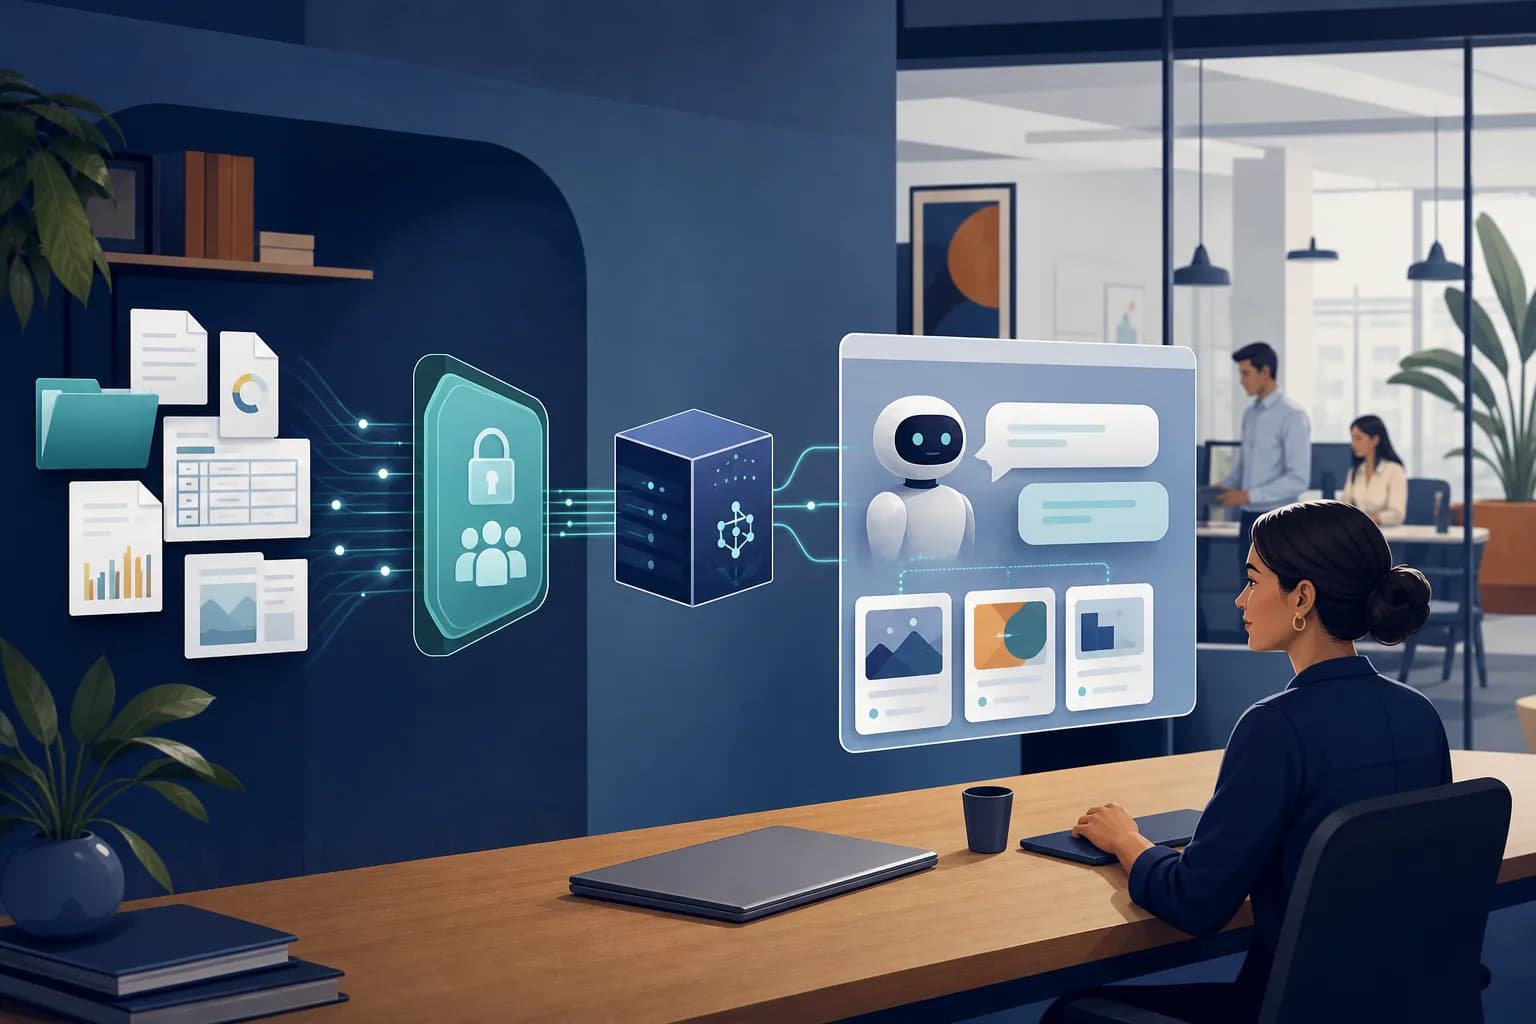
Before choosing a vendor, map the information flow: user, application, documents accessed, model, connected tools, and activity logs. Include intermediary services; a WhatsApp conversation may pass through several components before reaching your system.
Security and privacy are not the same. Security protects against unauthorized access and changes. Privacy also requires justifying why personal data is used, limiting its processing, and respecting individuals' rights over their data.
Classify the information that will flow through the integration:
| Information | Examples | Initial control |
|---|---|---|
| Public | Published catalogs and business hours | Verify that information is current and accurate |
| Internal | Procedures and operating manuals | Access by role and department |
| Confidential | Contracts, margins, and strategies | Restrictions by user and project |
| Personal or sensitive | Phone numbers, identification documents, and health data | Data minimization and legal review |
Also define what is out of scope. A bot that provides shipment status does not need access to a customer's entire financial history. Reducing the available data limits exposure and makes testing easier.
2. Evaluate vendors beyond their promises
Do not assume that an enterprise account, an API, or a model installed on your servers will solve AI data privacy concerns on its own. Each option distributes responsibilities differently.
Request documented answers on these points:
- Training: Are inputs, files, or responses used to improve models? What terms and settings apply?
- Retention: How long are conversations, files, logs, and backups retained? How do you request their deletion?
- Location: Where is information processed, and what other vendors are involved?
- Access: Which personnel can review content, and how is that access logged?
- Incidents: How do they notify you of a data exposure, and what support do they offer to investigate it?
- Exit: How do you retrieve your information and revoke access when the service ends?
Ask for answers specific to the product and plan you are purchasing, rather than a general marketing page. A policy of “not using data for training” does not necessarily mean there is no temporary storage.
Certifications can provide evidence, but review their scope. They do not replace an assessment of your integration, its permissions, or contractual obligations for confidentiality and data processing.
3. Apply controls to documents, conversations, and actions
Internal documents: respect existing permissions
In a RAG solution, the assistant retrieves document excerpts to answer questions. The risk arises when it searches information the user should not be able to see.
Authorization must be verified before content is retrieved and enforced for every query. If someone cannot open a record in the original system, they should not be able to obtain its contents by asking the assistant either.
Treat indexes and vector representations as information that requires protection, not as anonymous data by default. Also define how to update permissions and remove content when a document changes or is deleted.
WhatsApp and CRM: verify identity before revealing data
A phone number is not always enough to authorize a sensitive operation. With enterprise AI agents and chatbots, separate general guidance from inquiries about accounts, payments, or records.
For example, a bot can explain a return policy without additional authentication. To change a bank account used for deposits, it must move the operation to a secure workflow, with identity verification and approval based on risk.
Avoid requesting passwords or complete credentials in conversations. Mask personal data in logs when it is not needed for support.
Connected agents: limit what they can execute
An email, PDF, or message can contain malicious instructions directed at the model. This risk, known as prompt injection, attempts to make the assistant ignore its rules, reveal information, or misuse tools.
Writing “do not share data” in the prompt is not enough. Implement controls outside the model:
- Least-privilege credentials and explicitly authorized tools.
- Parameter and permission validation in the system that executes each action.
- Human approval for payments, deletions, and critical changes.
- Restrictions on destinations to which it can send information.
- Encryption in transit and at rest, with secrets kept out of prompts and code.
For AI process automation, start with read-only access or draft generation. Enable autonomous actions based on test evidence, not just because a demo worked.
4. AI and data protection in Mexico: review your obligations
If your private-sector business processes personal data in Mexico, consider Mexico's Federal Law on the Protection of Personal Data Held by Private Parties and other applicable provisions. Integrating AI does not remove existing obligations or make every use of information permissible.
With legal guidance, review at least the following:
- Purpose and privacy notice: Confirm that they adequately describe the planned data processing.
- Consent: Identify when it is required and what conditions apply, especially for sensitive data.
- Vendor relationships: Define responsibilities and distinguish processing on your behalf from potential data transfers.
- ARCO rights: Prepare mechanisms to handle access, rectification, cancellation, and objection requests across the systems involved.
- Retention: Establish retention and deletion schedules based on applicable purposes and obligations.
Do not assume that storing information outside Mexico is always prohibited or always permitted. The assessment depends on the data flow, contracts, and applicable regulations. If you serve customers in the United States, also review requirements tied to the industry, jurisdiction, and commercial agreements.
This review should take place before using real data, especially in healthcare and financial services.
5. Launch a pilot with approval criteria
Choose a narrowly scoped process, such as searching operating manuals that contain no personal data. Assign business, technology, and privacy owners; document who can approve changes and suspend the integration.
Before going live, test adverse scenarios:
- A user requests documents from another department.
- A file attempts to instruct the agent to send information to an external recipient.
- A customer asks to execute an operation without completing the required verification.
- A document's permissions change, or the document is deleted.
- The model or a tool becomes unavailable.
Verify that the defined cases result in blocks, authorization requests, or safe responses, as appropriate. Log denied access and executed actions without unnecessarily storing complete conversations.
Also define an incident response procedure: disable tools, revoke credentials, preserve evidence, and assess applicable notification requirements. Repeat testing when the model, document sources, or permissions change. An approved pilot does not guarantee that future changes will maintain the same level of protection.
6. Conclusion: integrate AI with verifiable boundaries
Enterprise AI security depends on controlling data, permissions, and actions throughout operation. Choosing a vendor is only one part: you also need clear contracts, adversarial testing, and the ability to stop the system when something goes wrong.
If you are considering connecting AI to WhatsApp, internal documents, or business management systems, contact Slashweb to discuss your project. We can help you define the use case and design an integration with controls appropriate to the risks and your business needs.
Frequently asked questions
How can you prevent employees from using AI tools without authorization?
Create a brief policy specifying which tools are authorized and what information must not be uploaded. Pair it with training and an approved alternative that meets real needs; banning tools without offering options can encourage unsupervised use.
Can anonymized data be shared with any AI model?
Not automatically: removing names may be insufficient if other attributes can identify an individual. Assess the risk of reidentification, and remember that the information may still be commercially confidential.
Is using an open-source model more secure?
Not by itself. It may offer greater control over deployment, but your business must manage updates, vulnerabilities, infrastructure, and access; security depends on how the solution is operated.
What metrics help evaluate the security of an AI integration?
You can track blocked unauthorized access attempts, sensitive operations performed without authorization, and the time needed to revoke access. Interpret these metrics alongside controlled test results: the absence of alerts alone does not prove that the system is secure.
Slashweb
Want to apply this in your company?
Book a free call with a specialist and get a tailored proposal.